Cyber Security Leader & Strategist
Hi, I'm Kishore Kumar
From audit to action — designing practical security that organizations can actually implement.
About Me
Building Security That Works
Eight years in IT, the last five dedicated entirely to cybersecurity. I started out building and running systems -- networks, servers, web platforms -- then moved into securing and governing them. That path is why I design controls engineering teams can actually live with.
Today I lead the security function for a software company in Dubai. I own the cybersecurity strategy, the annual IT budget, the security roadmap and the KPIs my team is measured against -- covering ISO 27001, SOC readiness, vendor selection and organization-wide risk.
I have not stopped being hands-on. Zero Trust identity, FortiGate and firewall policy, Wazuh SIEM, AWS hardening and penetration testing against our own applications are all still my work, not just my oversight.
Before security, I built 50+ websites as a freelance developer -- that background gives me a practical perspective on application security and secure code practices.
Dubai, UAE
Security Strategy & Governance
For Consulting
Impact
Measured Outcomes
Security Posture Uplift
Microsoft Secure Score improvement through Zero Trust hardening
Cyber Risk Reduced
Measured across organization-wide risk assessments
Faster Incident Response
Achieved via unified SIEM and NOC monitoring
Downtime Reduced
Resilient architecture and disaster-recovery planning
Applications Pentested
In-house products assessed and remediated
Figures reflect improvements delivered across the environments I have been responsible for. Specific baselines and client details are kept confidential.
Lead IT and Security Engineer
NEXSYS-ONE DMCC, Dubai
Promoted from Senior Network Administrator to lead the security function of a software company building custom ERP applications — accountable for security across cloud, network, endpoint and application layers, and for the team that delivers it.
- Own the annual IT and security budget — forecasting, licensing negotiation and cost optimization
- Define the yearly security roadmap, initiatives, KPIs and success metrics for the team
- Led ISO 27001 implementation and the 2013 → 2022 upgrade; support ISO 9001 and QMS audits
- Migrated Active Directory to Entra ID with Zero Trust endpoint hardening and conditional access
- Built SIEM and NOC capability on Wazuh, Zabbix and Uptime Kuma for 24×7 monitoring
- Evaluate and procure security products (PAM, DLP, SIEM) — from proof-of-concept to vendor negotiation
- Drive awareness across Development, QA, IT, HR, Accounts, Marketing and Project Management
Cyber Security Solution Expert & System Analyst
MAST Consulting Group, Dubai
Delivered security solutions across managed-service clients — VAPT, SOC and NOC build-outs, privileged access, ITSM and ISO 27001 compliance.
- Configured and managed FortiGate firewalls, VPNs and network segmentation policies
- Performed vulnerability assessments and penetration testing on client networks and web applications
- Deployed and operated client Security Operations Centres for proactive threat detection
- Established Network Operations Centres for continuous monitoring and analysis
- Drove ISO 27001 (2013 and 2022) compliance — risk assessments, gap analysis and awareness training
- Implemented PAM and ITSM platforms to protect critical assets and optimize service delivery
Web Developer
Freelancing
Built 50+ WordPress sites with custom themes and plugins, optimized for performance and SEO.
- Delivered end-to-end solutions spanning hosting, design, optimization and ongoing support
- Improved site performance by up to 70% through caching, image optimization and database tuning
- Hardened WordPress with firewalls, malware scanning and recurring security audits
- Developed dynamic PHP features including galleries, forms and file upload workflows
BE Computer Science Engineering
Hindusthan Institute of Technology, India
Bachelor of Engineering in Computer Science with a focus on networking and security fundamentals. CGPA 8.1.
Credentials
Certifications & Skills
Microsoft Cybersecurity Architect Expert
Jul 2025
Certified Ethical Hacker (CEH v11)
Apr 2021
ISO 27001:2022 Lead Auditor
Mar 2024
Microsoft Identity & Access Administrator
Jul 2024
ISC2 Certified in Cybersecurity
Jan 2023
CNSS Certified Network Security Specialist
Aug 2020
ICTTF Ransomware Uncovered Specialist
Mar 2023
Frameworks & Standards
Toolbox
Tools & Technologies
VAPT & Vulnerability Management
SIEM, NOC & Monitoring
Identity & Endpoint
Microsoft 365 Administration
Network & Firewall
Privileged Access Management
Cloud & Cloud Security
ITSM & Asset Management
Platforms & Virtualization
AI in Practice
Engineering with AI, Governed Like Everything Else
AI changed how much one security team can build. I use it to close the gap between the tools that generate data and the people who need to act on it — while applying the same governance to AI that I would apply to any other vendor in the estate.
AI as a Governed Engineering Practice
I do not treat AI as autocomplete. Every project I build with AI assistance carries a canonical context set — an instructions file defining the domain model and security constraints, org-wide coding guidelines, and a decisions log. The rule is simple: no code is written until that context has been read, security is stated as the primary design constraint rather than an afterthought, and nothing reaches a protected branch without human review. It turns an unpredictable tool into a repeatable one.
Custom Tooling for Reporting & Visibility
Security tools produce raw output; leadership needs decisions. I build the layer in between. Scanner JSON becomes an executive report with severity breakdowns and CVSS context. SIEM alerts become tracked Jira tickets with owners and SLAs. Findings scattered across several products become the Argus Security Dashboard — one place to see posture, correlate causes and act, behind SAML SSO and role-based access.
AI in Security Operations
AI compresses the slow parts of security work — summarising alert context across tools, drafting policy against ISO 27001 and SOC control language, writing detection logic and turning assessments and incidents into readable reports. I use it to move faster on the analysis and documentation load, while keeping judgement, verification and sign-off human. Speed on the writing, not on the deciding.
Securing How AI Gets Used
Adopting AI is itself a risk decision. The same governance I apply to any vendor applies here — what data leaves the organization, where it lands, who approved it and what the fallback is. Secrets stay out of prompts and inside a managed store with scoped tokens and full access logging, dependency and code quality scanning runs inside the repositories themselves, and awareness training now covers AI-assisted phishing and social engineering.
What I Do
Specializations
Security Strategy & IT Budgeting
Annual security roadmaps, IT budget ownership, initiative planning and cost optimization aligned to business goals.
Governance, Policy & KPI Design
Security policies and ITIL-based procedures, security metrics, and team KPIs that make performance measurable.
Cybersecurity & Risk Management
Risk assessments, threat modelling, and security roadmaps aligned with business objectives.
Compliance & Audit Readiness
ISO 27001 (2013 → 2022 upgrade), ISO 9001, SOC 1 and SOC 2 readiness, gap analysis, and remediation.
Zero Trust Architecture
Identity-first design, conditional access and MFA, endpoint hardening and Microsoft Secure Score uplift.
Vendor Management & Procurement
Product evaluation (PAM, DLP, SIEM), proof-of-concepts, vendor negotiation and procurement.
Identity & Access Management
Azure Entra ID, Intune MDM, conditional access policies, and SSO integration.
Privileged Access & Firewall Management
FortiGate, Sophos firewall rules, PAM solutions, and network segmentation.
Penetration Testing & VAPT
Nessus, Burp Suite, Metasploit, ZAP — full vulnerability assessment and reporting.
Cloud Security Engineering
AWS and Azure hardening, cloud security assessments with Prowler and Scout Suite, Linux and Windows server security.
SIEM & Monitoring Operations
Wazuh, DNIF, Zabbix, Uptime Kuma, Nagios — log correlation, alert tuning, and incident response.
IT Operations & Service Management
ITSM platforms (Ivanti, Jira, osTicket) setup, SLA management, and process automation.
Security Awareness & Training
Phishing simulations, security workshops, and policy documentation for teams.
Web Development & Optimization
WordPress, Next.js — performance optimization, security hardening, and custom development.
AI-Assisted Platform Engineering
Building internal platforms and tools with AI in the loop — governed by written context, coding standards and human review gates.
Security Automation & Custom Tooling
Turning scanner and SIEM output into decision-ready reporting — alert-to-ticket automation, executive vulnerability reports and operations dashboards.
Blog
Recent Posts
View All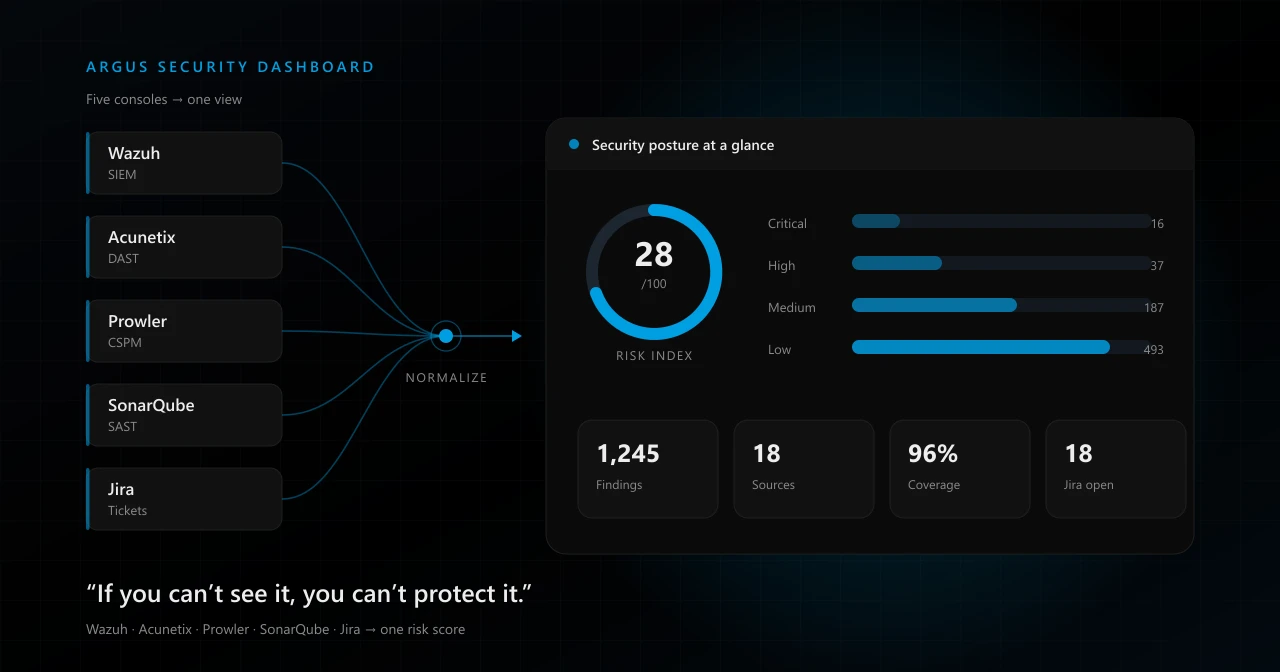
If You Can't See It, You Can't Protect It — Building the Argus Security Dashboard
How we went from no visibility, to too many tools, to a scattered-data problem — and ended up building a single security posture dashboard with an organization-wide risk score.
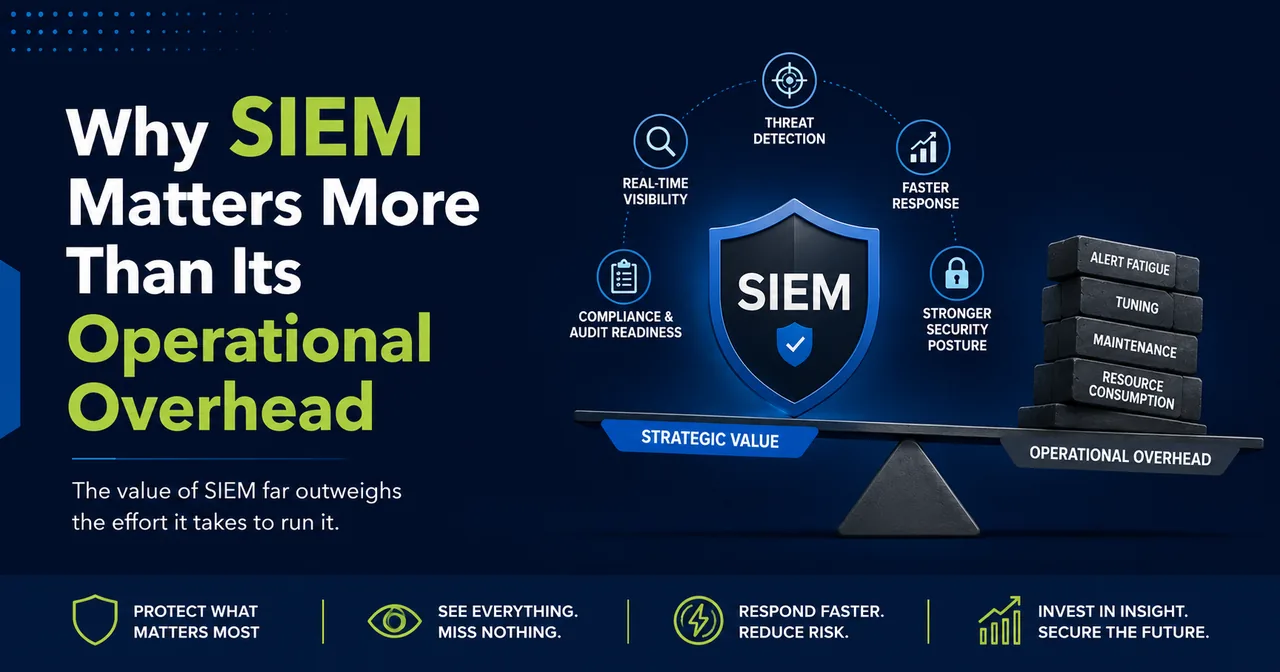
Why SIEM Is More Important Than Its Operational Overhead
Most teams look at SIEM and see cost, noise, and maintenance. But the real question is whether you can afford to operate without centralized visibility, detection, and log retention.
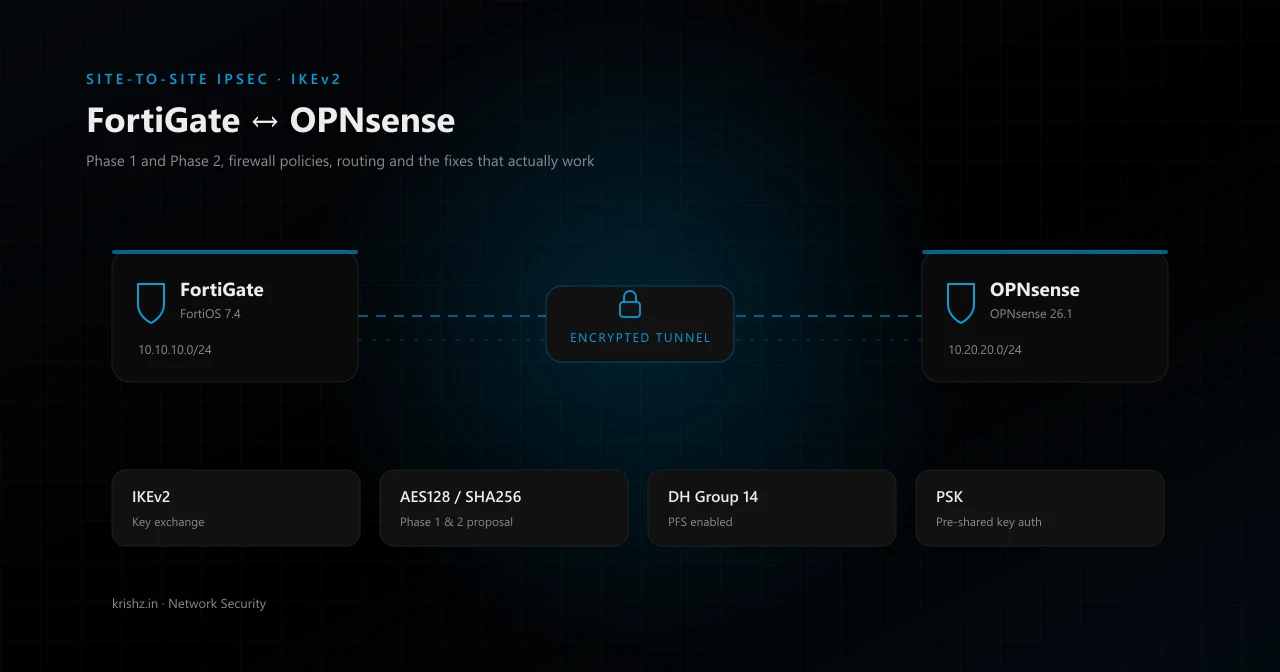
Building a FortiGate to OPNsense Site-to-Site IPsec Tunnel with IKEv2
Step-by-step FortiGate to OPNsense site-to-site IPsec tunnel guide using IKEv2, AES128/SHA256, PSK, firewall policies, routing and troubleshooting.
Contact
Get in Touch
Have a project in mind or need a security consultation? I'm always open to discussing new opportunities and challenges.